
I think it says something when an entire industry of competing hardware wallet makers, including Ledger, companies that rarely coordinate on anything publicly, all rush to say the exact same thing within hours of each other: not us, not our devices, not our problem.
That’s exactly what happened today. Bitkey, Ledger, Trezor, Jade, and Tangem all moved quickly to reassure their own users they were unaffected by a specific hardware wallet failure.
The wallet at the center of that failure is Coldcard, and the reason everyone else felt compelled to speak up is a $38 million theft that traces back to a flaw sitting quietly in its firmware.
Why Every Other Wallet Maker Rushed To Speak Up
In the hours following news of the exploit, hardware wallet manufacturers moved fast to distance themselves from whatever had gone wrong. Ledger stated plainly that it was not affected by the recently published Coldcard Mk3 advisory, pointing to its certified True Random Number Generator built directly into its Secure Element chip, which it says generates the full 256 bits of entropy required for every 24-word recovery phrase. Tangem issued a similar reassurance to its own users, while Trezor and Jade echoed the same message across their own channels, each asserting their entropy generation processes were untouched by whatever caused Coldcard’s failure.
I think this wave of near-simultaneous reassurance tells you how seriously the industry is treating this incident, even among direct competitors. Nobody wanted to be the wallet maker who stayed silent while users of every other brand were quietly wondering if their own seed phrase was next. But I’d also read these statements with a bit of caution. At this stage, every one of these companies is largely trusting their own prior audits rather than responding to fresh, independent verification triggered specifically by this incident.
The Scale Of What Actually Happened To Coldcard
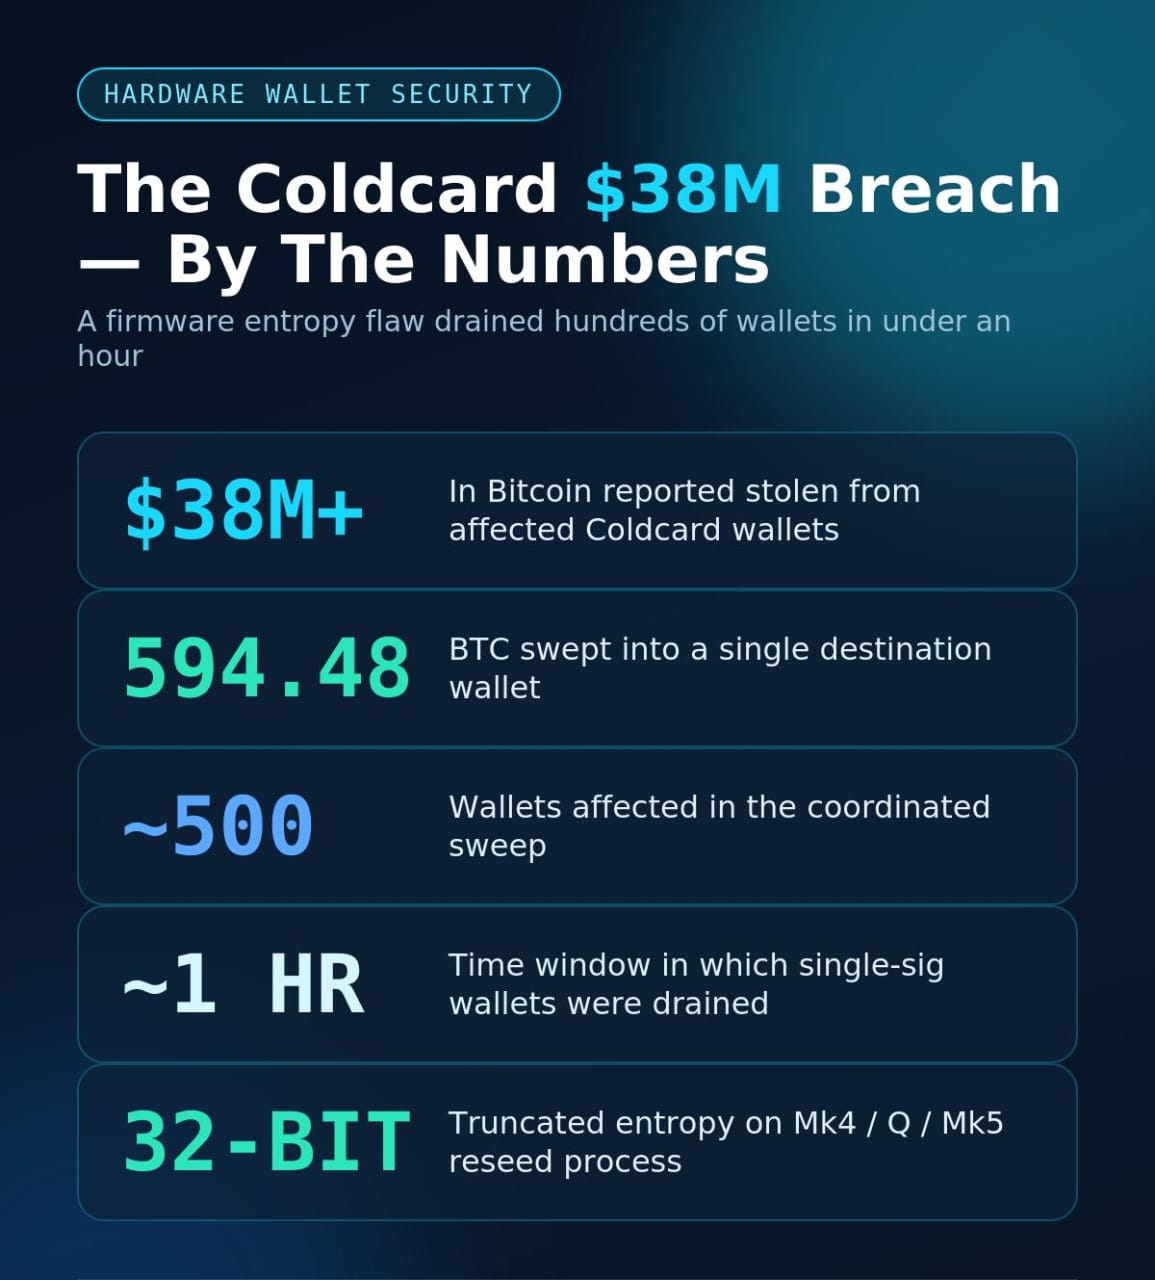
So what exactly are all these companies distancing themselves from? More than $38 million worth of Bitcoin has reportedly been stolen through a Coldcard wallet exploit, with around 500 wallets affected and a combined 594.48 BTC swept into a single destination wallet. I think the concentration into one wallet is worth sitting with. This wasn’t scattered, opportunistic theft. It was a coordinated sweep against a specific, identifiable pool of vulnerable devices.
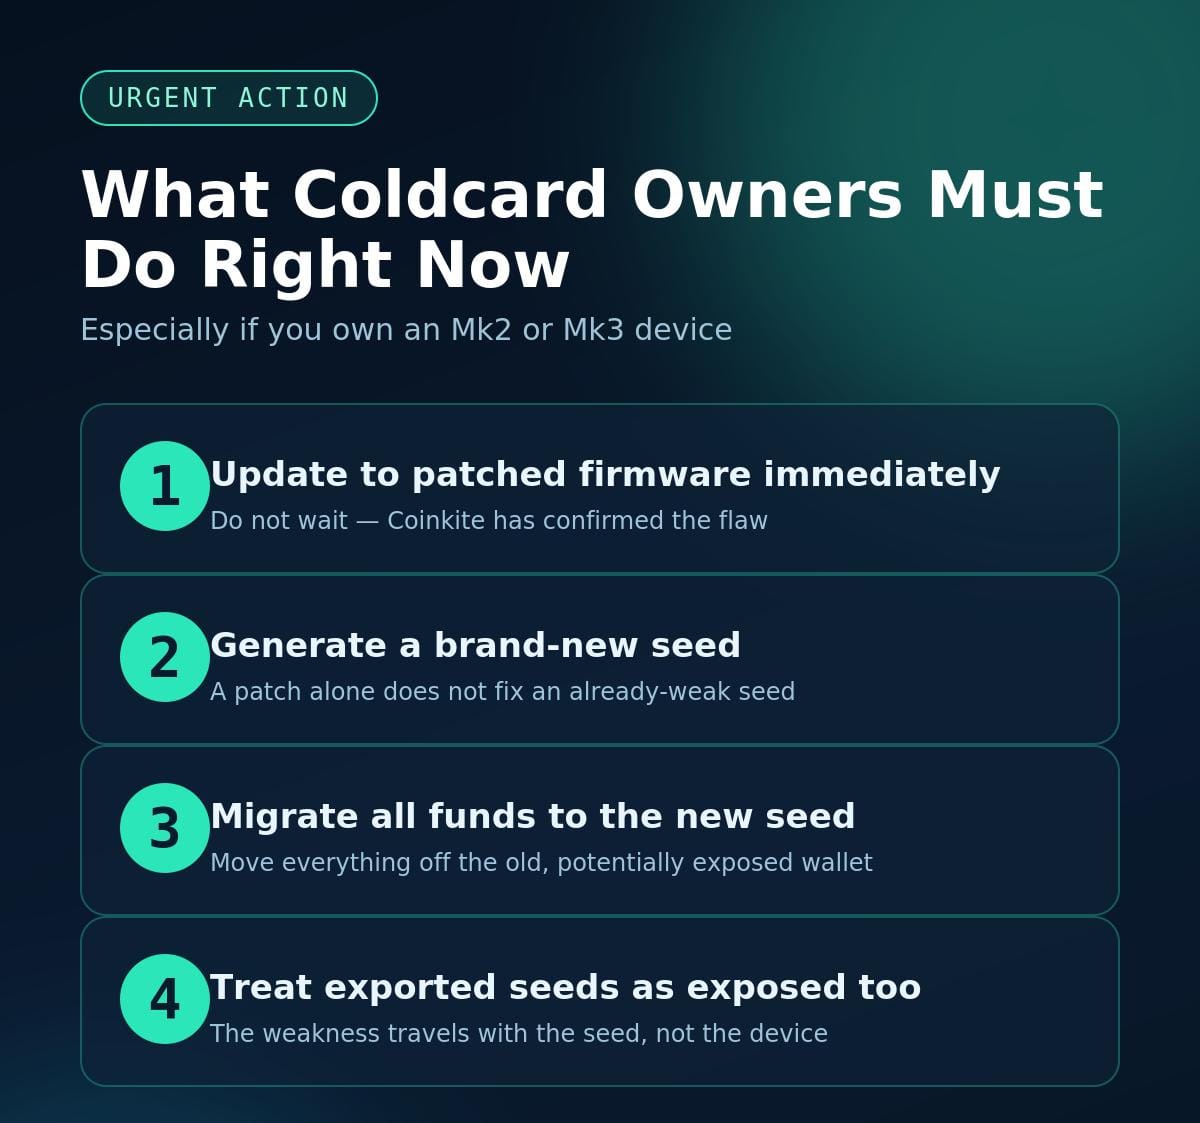
Coldcard’s manufacturer, Coinkite, confirmed the underlying problem directly, disclosing a critical entropy-generation flaw affecting Coldcard firmware. The vulnerability may have reduced the effective randomness behind seeds generated on affected Mk2 and Mk3 devices, and Coinkite linked it directly to the reported theft. Its guidance was blunt: if you generated a seed using affected firmware, update to patched firmware, generate an entirely new seed, and migrate your funds away from anything touched by the old one.
I think the instruction to generate a brand-new seed, rather than simply patching and continuing with the existing one, tells you how seriously Coinkite is treating this. A patch fixes future seed generation. It does nothing to fix a seed that was already generated with insufficient randomness before the patch existed.
Block’s Investigation Uncovers Two Separate Bugs
The most detailed technical breakdown came from an unexpected source: Block, the parent company behind the competing Bitkey wallet, whose security team began investigating reports of non-Bitkey wallets being drained the moment they surfaced. Block’s team was upfront that no Block products, including Bitkey, were affected, but continued investigating specifically to protect anyone holding Bitcoin in self-custody regardless of which wallet they use.
What they found was two distinct vulnerabilities. Initially, only single-signature wallets were drained remotely over roughly an hour, and Block warned the attack is likely ongoing, meaning more wallets could be hit, including those using 25th-word passphrases that are too weak and multisig setups where more than one key was generated insecurely. On Mk2 and Mk3 devices specifically, the firmware intended to use the hardware’s random number generator to create keys, but a mistake in a firmware macro caused it to rely instead on a known device UID, timer state, and call history, making wallet generation deterministic rather than genuinely random. Mk4, Q, and Mk5 devices attempted to compensate at boot using secure-element input, but the reseed process truncated that input down to just 32 bits, sharply limiting the actual secret entropy contributed, far below what a wallet should have.
Block noted that if a seed was originally generated on a vulnerable Coldcard and later exported to a completely different wallet, that same insecure seed remains compromised regardless of where it currently lives. The team said they disclosed these findings to Coinkite as soon as possible, and Coinkite acknowledged them, before Block chose to go public specifically to protect the broader self-custody community rather than sit on the information.
The Attacker’s Costly Mistake
Here’s the detail I think deserves far more attention than it’s currently getting. Bitkey’s engineering lead shared a finding from the investigation into the drain that could genuinely matter for tracing whoever’s responsible. While reviewing the sweep pattern, the team noticed something unusual, and confirmed a hypothesis: the operator used a paid account at a well-known blockchain-services provider to query the source addresses and carry out related activity during the sweeps.
I think this is a genuinely significant operational security failure on the attacker’s part. Running queries through a paid, presumably KYC-linked account while executing a $38 million theft is the kind of mistake that professional investigators live for. It doesn’t guarantee identification, but it gives law enforcement and researchers like ZachXBT a concrete thread to pull that a fully anonymous attack wouldn’t have offered.
What Coldcard Owners Need To Do Right Now
If you own a Coldcard, especially a Mk2 or Mk3 device, I don’t think this is a wait-and-see situation. Update to patched firmware immediately, generate a completely new seed rather than continuing with your existing one, and migrate any funds tied to a seed that could have been generated before the patch. If you ever exported that seed into a different wallet, treat those funds as exposed too, since the underlying weakness travels with the seed itself, not the device that originally created it.
I think the broader lesson here extends past Coldcard specifically, and past the reassurances coming from Ledger, Trezor, Jade, and everyone else this week. Hardware wallets are trusted precisely because users assume the randomness underneath their seed phrase is unimpeachable. This incident is a reminder that even that foundational assumption deserves periodic, independent scrutiny, and that when a flaw like this does surface, the difference between a $38 million loss and a contained incident often comes down to how fast the company discloses it and how clearly it tells affected users exactly what to do next.
Disclosure: This is not trading or investment advice. Always do your research before buying any cryptocurrency or investing in any services.
Follow us on Twitter @themerklehash to stay updated with the latest Crypto, NFT, AI, Cybersecurity, and Metaverse news!